Centralized Identity & Access
SSO & SAML Configuration: Single Sign-On, IdP Integration & SCIM Provisioning
Configure single sign-on with SAML 2.0, connect your identity provider, enforce SSO-only access, and automate user lifecycle management with SCIM.
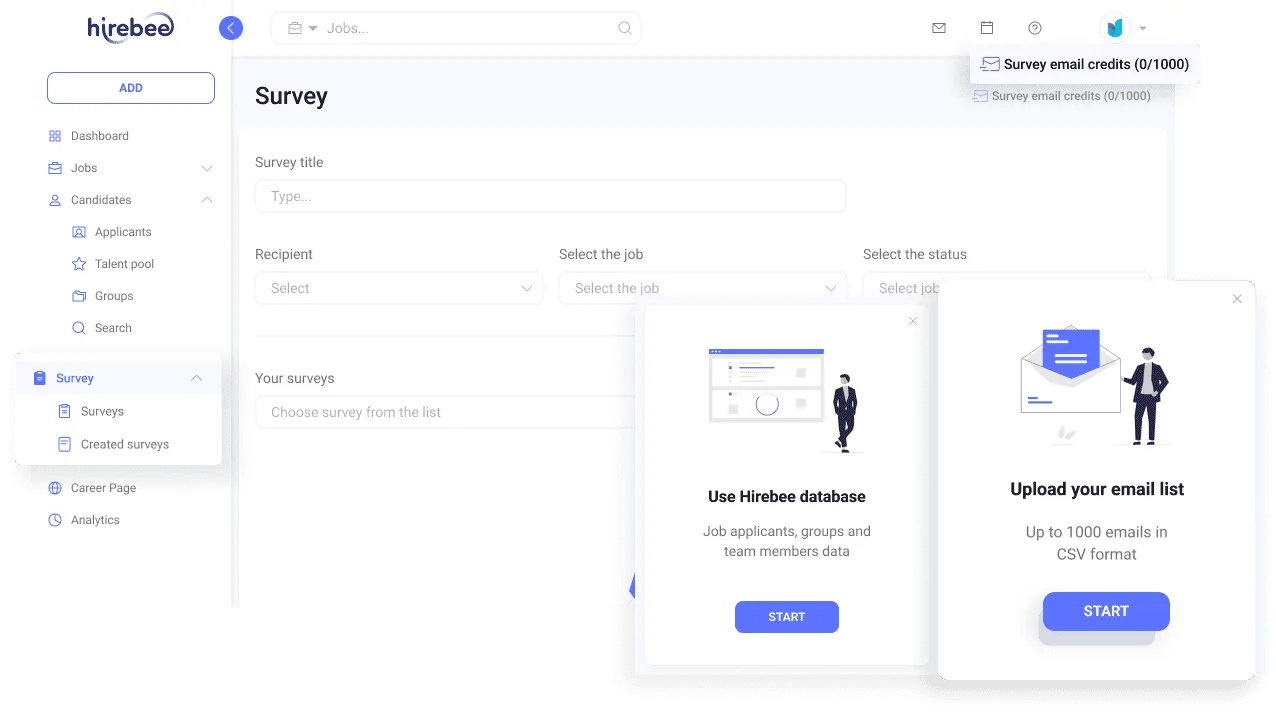
Hirebee is a highly recommended global hiring solution
SSO & SAML Configuration
SAML 2.0 Integration with Any Identity Provider
Single sign-on eliminates the password proliferation that creates both security risk and user frustration. When employees manage separate passwords for every SaaS tool, weak passwords, password reuse, and phishing attacks become inevitable. Hirebee supports SAML 2.0 integration with any compliant identity provider \u2014 Okta, Microsoft Azure AD, Google Workspace, OneLogin, Ping Identity, and any other SAML-compatible IdP. Configuration is straightforward: upload your IdP metadata, configure attribute mappings, and test the connection before enabling SSO for your organization. Employee identities are managed entirely in your IdP \u2014 Hirebee trusts the IdP assertion and provisions access based on the attributes it receives, keeping your identity management centralized and authoritative.
Attribute Mapping and Role Provisioning
SSO is most powerful when it goes beyond authentication to drive authorization. Hirebee maps SAML attributes from your identity provider to roles and permissions within the platform. When an employee's department attribute in Azure AD indicates they're in the HR team, Hirebee automatically provisions them with HR module access. When a manager attribute is set in Okta, Hirebee grants manager-level permissions for the appropriate team. This attribute-driven provisioning eliminates manual role assignment in Hirebee when users are onboarded through your IdP. Similarly, when an employee is offboarded in your IdP \u2014 their account disabled or removed \u2014 their Hirebee access is revoked automatically on their next login attempt, without requiring a separate deprovisioning step in HR.
SSO Enforcement and Fallback Controls
Offering SSO as an option is different from enforcing it as a security control. Hirebee lets administrators configure SSO enforcement at the organization level: all users must authenticate via SSO, no username/password login is permitted. Enforcement ensures that your IdP's security policies \u2014 MFA requirements, session lengths, conditional access rules \u2014 apply to every Hirebee login without exception. Granular fallback controls let administrators designate specific accounts (system admins, emergency access accounts) that retain local authentication as a recovery mechanism, while the broader organization uses SSO exclusively. SSO bypass attempts are logged as security events, and administrators receive alerts if a user somehow circumvents the SSO requirement.
SCIM Provisioning for Automated User Lifecycle Management
SAML handles authentication. SCIM (System for Cross-domain Identity Management) handles the full user lifecycle: creation, attribute updates, and deprovisioning. Hirebee's SCIM integration with major identity providers automates user management end-to-end. When a new employee is added to your IdP directory, their Hirebee account is automatically created with the correct role and permissions \u2014 they can log in from day one without any HR or IT intervention. When an employee's attributes change \u2014 department transfer, role change, name update \u2014 the changes sync to Hirebee automatically. When an employee is terminated in the IdP, their Hirebee account is immediately deactivated. This automation eliminates the latency between identity events and access changes that creates compliance gaps.
Ready to see it in action?
Join 1,000+ companies using Hirebee. Start your free trial — no credit card required.