One Identity. Every Application.
SSO & Identity Integrations: SAML 2.0, SCIM Provisioning & Directory Sync
Connect any SAML 2.0 identity provider, automate user provisioning and deprovisioning with SCIM 2.0, and keep organizational structure synchronized across your entire HR platform.
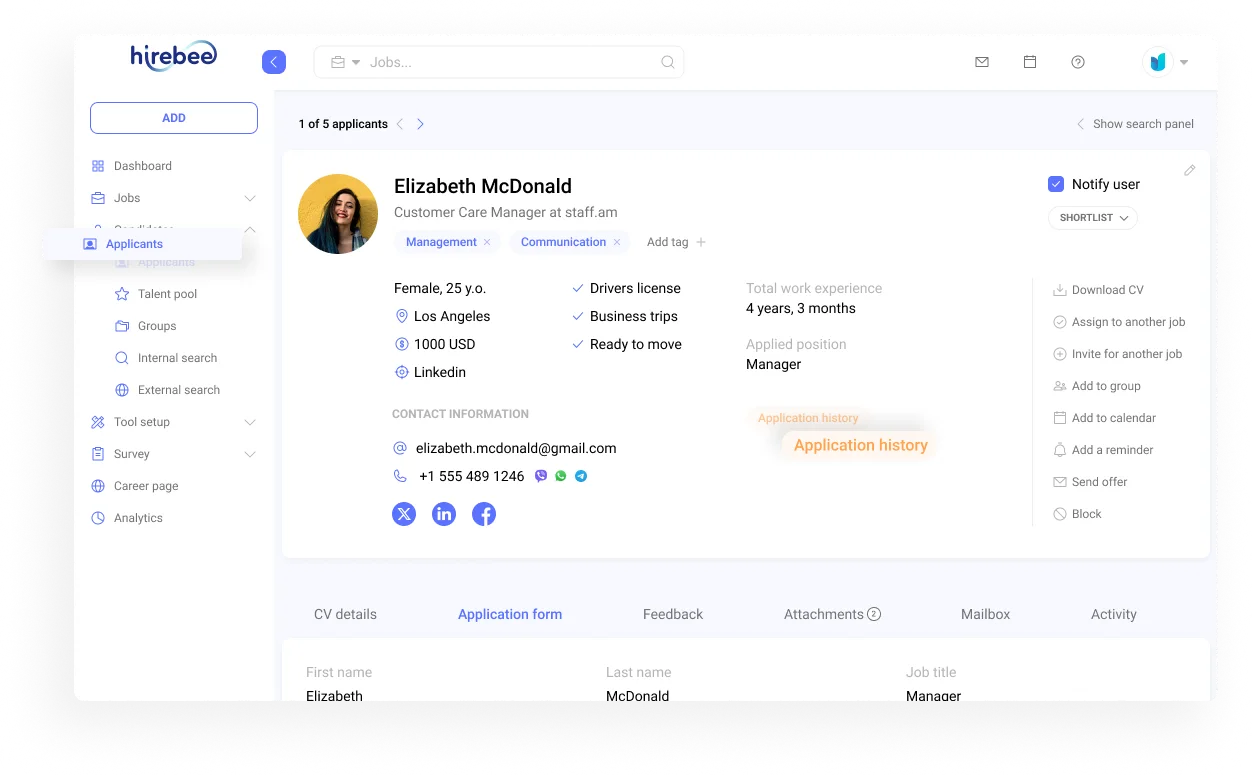
Hirebee is a highly recommended global hiring solution
SSO & Identity Integrations
SAML 2.0 Integration with All Major Identity Providers
Enterprise organizations manage employee identities through centralized identity providers — Okta, Microsoft Azure AD, Google Workspace, OneLogin, Ping Identity, JumpCloud — and expect every SaaS application to authenticate through these systems rather than maintaining separate credentials. Hirebee's SAML 2.0 implementation supports all standards-compliant identity providers without custom development: upload your IdP metadata, map the SAML attributes your provider sends to Hirebee's user profile fields, test the connection in a sandbox environment, and enable SSO for your organization with a single configuration toggle. The setup process is guided and typically completes in under an hour for standard identity providers. For organizations with multiple IdPs — common in post-acquisition environments where different business units run different identity infrastructure — Hirebee supports multi-IdP configuration, routing authentication requests to the appropriate provider based on the user's email domain. SSO enforcement can be configured globally (all users must use SSO) or selectively (SSO required for specific roles or locations while maintaining username/password as a fallback for others).
SCIM 2.0 Automated User Provisioning and Deprovisioning
Manual user account management in SaaS applications is a security and compliance liability. When a new employee joins, IT must remember to create their Hirebee account and assign the correct permissions — a step that gets missed, creating first-day access problems. When an employee leaves, their account must be deactivated in every application — a step that gets delayed or forgotten, leaving active accounts for former employees. SCIM 2.0 (System for Cross-domain Identity Management) eliminates both problems by automating the full user lifecycle directly from the identity provider. When a new employee is added to Okta, Azure AD, or any other SCIM-compatible IdP, their Hirebee account is automatically created with the correct role, department assignment, and permissions — without any manual action from IT or HR. Attribute mappings translate IdP attributes to Hirebee roles: an Azure AD group membership translates to a Hirebee manager role, a department attribute maps to a Hirebee cost center and access scope. When an employee is deactivated in the IdP, their Hirebee account is immediately disabled, their active sessions are terminated, and their data access is revoked — closing the offboarding security gap that manual processes routinely leave open for days or weeks.
Directory Sync and Organizational Structure Integration
Identity providers maintain authoritative records of organizational structure — who reports to whom, which teams employees belong to, what departments exist — and this structure should be reflected accurately in the HR system without requiring manual duplication and maintenance. Hirebee's directory sync reads organizational hierarchy data from the connected identity provider and keeps it synchronized: manager relationships, team memberships, department assignments, and reporting structures in Hirebee mirror the IdP directory automatically. When an employee is promoted and their manager field is updated in Azure AD, the change flows to Hirebee, updating the org chart, adjusting their manager's visibility into their records, and ensuring that HR workflows that route based on reporting structure operate on current data. For organizations undergoing restructuring, the directory sync means that HR system changes are driven by a single update in the identity provider rather than requiring parallel updates across multiple systems. Sync frequency is configurable — near-real-time for organizations with high employee movement, scheduled daily sync for more stable organizational structures — with conflict resolution rules that determine which system is authoritative when discrepancies are detected.
Federated Identity for Multi-Entity and M&A Environments
Corporate acquisitions, multi-subsidiary structures, and joint ventures create identity management complexity: multiple separate identity provider environments that need to be connected to a single HR platform without forcing full identity infrastructure consolidation — an exercise that often takes years and requires significant IT investment. Hirebee's federated identity support allows organizations to connect multiple IdPs to a single Hirebee instance, each serving a different entity, subsidiary, or business unit. Users from each entity authenticate through their own IdP, access the data scope appropriate to their entity, and coexist in the same HR platform without requiring identity infrastructure consolidation as a prerequisite. Cross-entity visibility is managed through permission configuration: an HR leader at the parent company can see data across all entities, while subsidiary HR teams see only their own data. This federated model makes Hirebee viable as the consolidated HR platform from day one of an acquisition, before the complex infrastructure work of identity consolidation is complete — and in some cases, it makes the identity consolidation work unnecessary altogether by managing the complexity at the application layer.
Ready to see it in action?
Join 1,000+ companies using Hirebee. Start your free trial — no credit card required.